Tags: GS Paper 3 – Science and Technology: Artificial Intelligence; Cyber Security
For Prelims: CERT-In, Section 70B of IT Act 2000, Agentic AI, Large Language Models, prompt injection, IndiaAI Mission, India AI Governance Guidelines, AI Safety Institute
For Mains: Governance of autonomous AI systems, cyber-security risks of AI agents, balancing innovation with accountability
Why in News?
The Indian Computer Emergency Response Team (CERT-In) has issued the “Artificial Intelligence (AI) Security Auditing Guidelines: Framework for Secure, Ethical, and Auditable AI Systems”. The guidelines include specific security and audit requirements for agentic AI systems, which are AI systems that can plan and carry out tasks on their own, use external tools, and delegate work to other AI agents.
Summary
- The guidelines name autonomous task execution, persistent memory and delegation as features that increase risk.
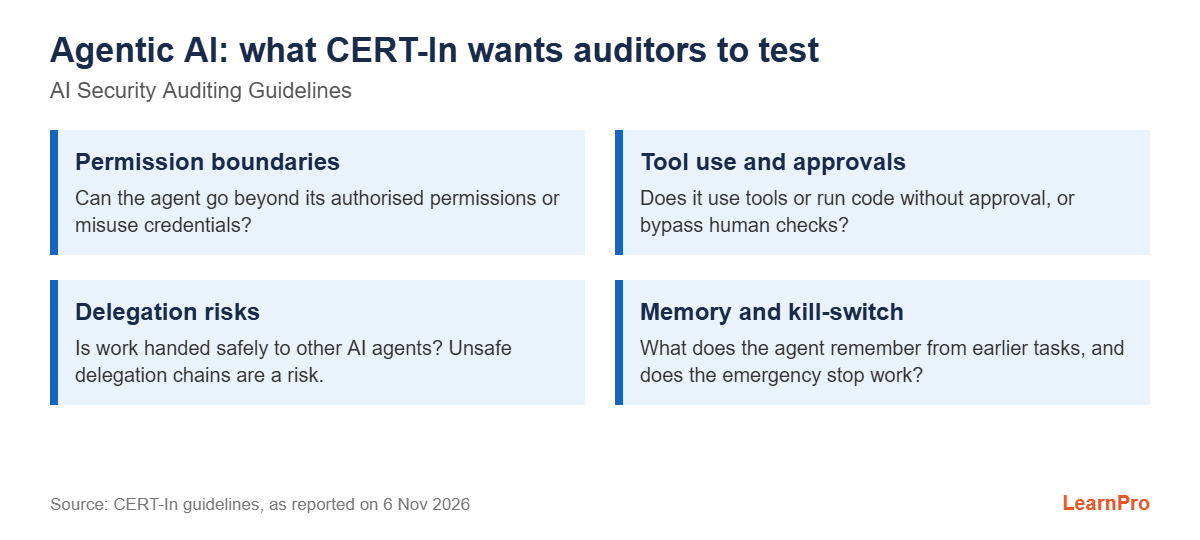
- Auditors must test whether an agent can exceed its permissions, use tools without approval, bypass approval steps or misuse credentials.
- They must also check for unsafe delegation, risks from the agent’s memory, and whether emergency-stop (kill-switch) mechanisms work.
What is Agentic AI?
- Conventional chatbots answer prompts. Agentic AI systems pursue goals over multiple steps. They break a task into parts, call software tools and APIs, run code, browse the web and coordinate with other agents.
- Examples: Coding agents, customer-service agents that issue refunds, and AI assistants that book travel or manage email.
- Core components: A foundation model (LLM) for reasoning, tools or actions, memory, and an orchestration layer.
Key Security Risks of Agentic AI
| Risk | What it means |
|---|---|
| Prompt injection | Hidden instructions in web pages, emails or files take control of the agent’s actions |
| Excessive agency | The agent has wider permissions than its task needs (violates the principle of least privilege) |
| Credential misuse | API keys and passwords stored by the agent are leaked or misused |
| Memory poisoning | Harmful data stored in the agent’s memory affects later tasks |
| Cascading delegation | Errors or compromise spread through chains of agents |
| Accountability gap | It is unclear who is responsible when an autonomous action causes harm |
About CERT-In
- CERT-In is the national nodal agency for cyber-security incident response under Section 70B of the IT Act, 2000. It works under MeitY.
- Its functions include collecting and analysing cyber incidents, issuing alerts, coordinating emergency response and empanelling security auditors.
- Its 2022 directions require cyber incidents to be reported within 6 hours.
India’s AI Governance Landscape
- IndiaAI Mission (2024): ₹10,372 crore for compute capacity, foundation models, datasets and skilling.
- India AI Governance Guidelines (2025): A principle-based, light-touch approach that relies on existing laws and voluntary frameworks.
- IndiaAI Safety Institute: Works on standards and testing for safe AI.
- Digital Personal Data Protection Act, 2023: Governs personal data used by AI systems.
Way Forward
- Require human-in-the-loop approval for high-impact actions such as payments, deletion of data and sending messages.
- Apply least-privilege access, sandboxing and complete action logs for audits.
- Carry out red-teaming and independent third-party audits before agents are deployed in critical sectors.
- Clarify liability rules for harm caused by autonomous AI systems.
Conclusion
As AI moves from answering questions to taking actions, the main security concern shifts from what a model says to what it can do. CERT-In’s guidelines are an early step towards making AI agents auditable, controllable and accountable.
Frequently Asked Questions (FAQs)
1. Under which law does CERT-In function?
Section 70B of the Information Technology Act, 2000.
2. How is agentic AI different from a chatbot?
It can plan multi-step tasks, use tools and act on its own, rather than only respond to prompts.
3. What is prompt injection?
An attack in which malicious instructions hidden in content take over an AI system’s behaviour.
Practice Question
Mains: Agentic AI systems pose new governance and security challenges. Discuss, with reference to India’s regulatory approach. (150 words)